Mirantis Agent Platform release notes#
Versions of the Mirantis Agent Platform Helm chart, newest first.
helm upgrade lens-agents oci://ghcr.io/lensapp/lens-agents --reset-then-reuse-values --wait
Database migrations run at startup. Sandboxes keep running across an upgrade and reconnect when the new server process is ready.
0.36.0 — 9 November 2026#
An install starts a 30-day evaluation when you activate it, until an owner enters a license key. nexusctl runs on Windows.
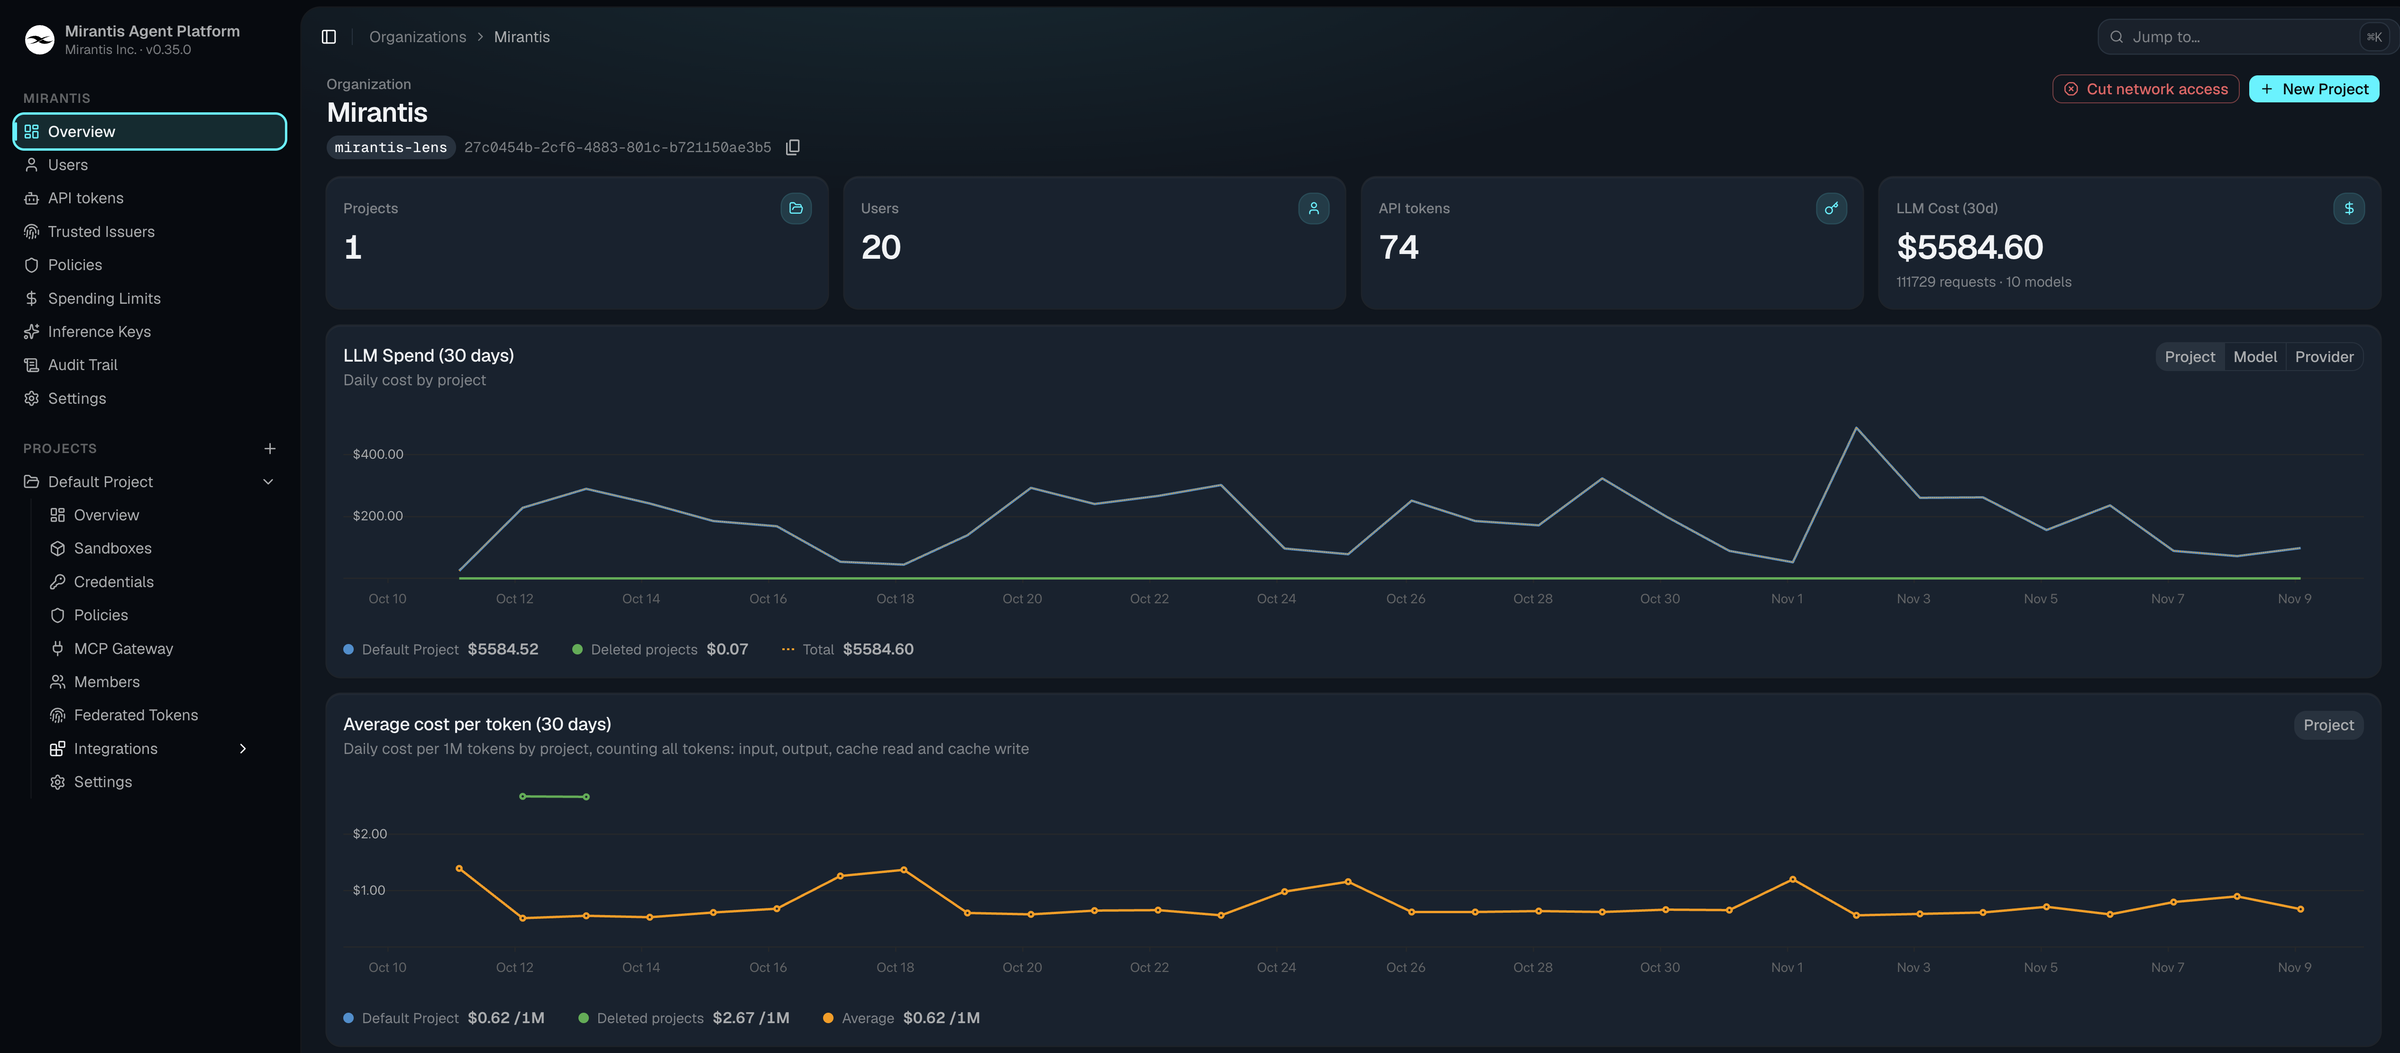
Mirantis Agent Platform. The web UI shows the Mirantis Agent Platform brand.
Activation and license. A new install asks for a name, company, work email, and the activation code from a Secret the chart generates, or activates itself from activation.activator values. It then runs for 30 days in evaluation mode. An installation owner enters the license key on the License page, with nexusctl installation license, or with license.* values. The key is checked inside the install. See Activation and license.
nexusctl on Windows. irm https://agents.example.com/install.ps1 | iex installs it from your server in PowerShell. See Set up the CLI.
Audit trail in the admin UI. Filters apply on the server, so every page holds only matching events, and the next page loads as you scroll. Jump to shows the trail at or before a chosen time. See Audit trail.
Sandboxes by name. nexusctl sandbox commands also find a sandbox by its name. See CLI reference.
Sandbox deletion events. Event webhooks also send sandbox.deleted. See sandbox.deleted.
Fixes:
- A malformed WebSocket upgrade request gets
400instead of stopping the server. It needed no authentication. - A sandbox whose agent runs out of memory restarts, instead of staying in
errorwith its ports answering502. A sandbox that fails soon after each start stops inerrorafter five attempts. - Responses through a Kubernetes cluster connection arrive complete, including the end of
kubectl execoutput. - The admin UI lets you edit a sandbox's name, labels, timers, policies, and credentials in every state.
nexusctlshows the cause when a command or a sandbox fails.- The server image updates
@hono/node-serverto 1.19.18, for GHSA-jpvv-r467-5p4w.
Before you upgrade
- Plan to activate. After the upgrade, the web UI shows the Activate screen once. Read the code with the command in the install notes, or set
activation.activatorvalues. Sign-in,nexusctl, MCP clients, and the API do not change. See Upgrading from Hub enrollment. - Upgrade with
--reset-then-reuse-values.--reuse-valueskeeps the old chart's values and fails on the newactivationvalues. - Remove the
hubvalues andoidc.useExternalProvider. They are no longer read.
0.35.0 — 2 November 2026#
Exposed ports can verify webhook senders, a sandbox agent can schedule its own wake, and event webhooks announce spending-limit thresholds. Spending limits can renew from a chosen date, and the admin UI has a new design.
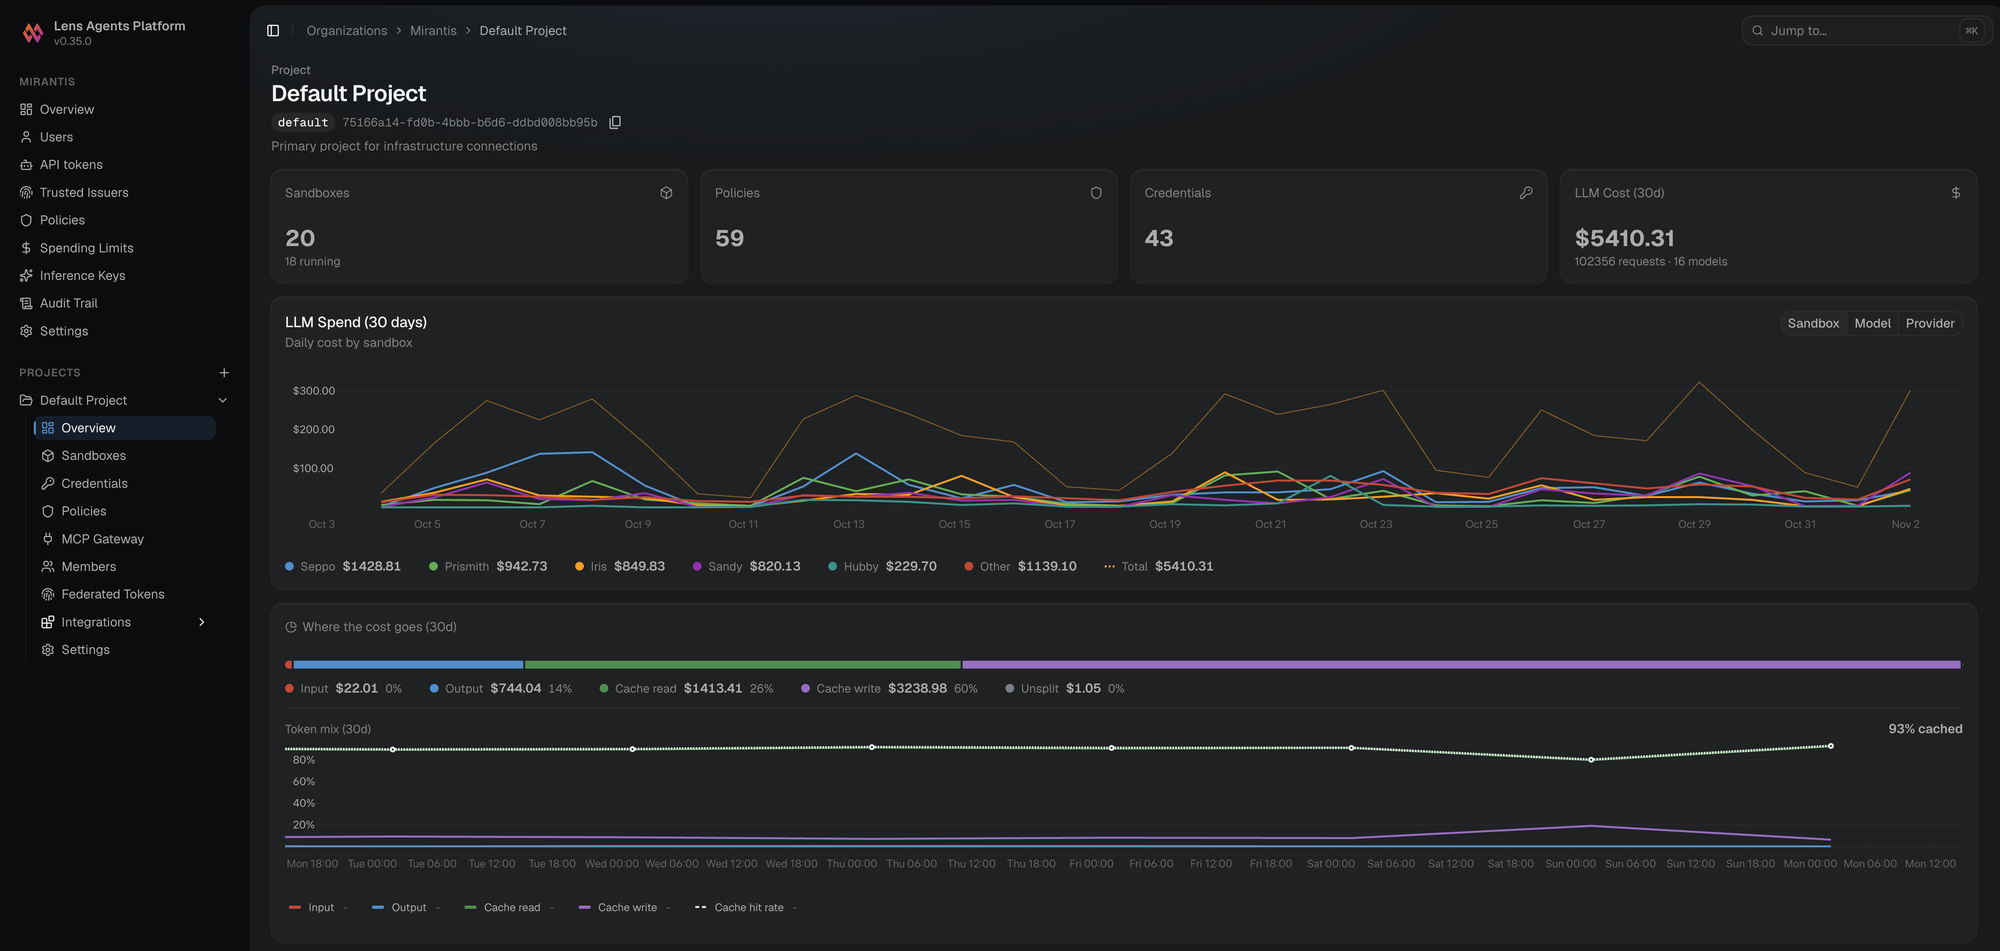
Webhook ports. A port with auth: webhook admits only requests that carry a shared token or an HMAC signature of the body, and answers any other request with 401 before it reaches the sandbox. Declare one with --port and --webhook-secret-file, a spec file, or the admin UI, and rotate its secret without a restart with nexusctl sandbox webhook-secret. See webhook.
API tokens on private ports. A request to a private port made with an API token carries the token's ID in x-forwarded-token-id. See private.
Scheduled wake. A sandbox agent calls the schedule_wake MCP tool with the time of its next task, and an auto-stopped sandbox with start on demand starts again shortly before it. See Wake on a schedule.
Model calls count as activity. A model call through the platform's LLM proxy keeps a sandbox from auto-stopping while it runs. See Stop and delete idle sandboxes.
Event webhooks. Access webhooks are now event webhooks, set under eventWebhooks, and receivers also get spending_limit.threshold when an org's spend reaches 80% or 100% of an org-level limit. See Event webhooks.
Spending-limit renewal. A limit can renew from a chosen whole UTC hour, such as a billing date, instead of the calendar. Set periodAnchor, nexusctl spending-limit set --anchor, or Renews in the admin UI. See Renew from a chosen date.
Ingress clients without a role. oidc.sandboxIngressClientsWithoutRole lists OIDC clients whose bearer tokens open private ports for org members with no realm role. See Direct API access.
Service account. oidc.serviceClients names a dedicated client whose client-credentials token is org admin in every organization. See Service account.
Fixes:
- Git fetch and push work again under an org ceiling with
*mid-path, such asPOST /*/*/git-upload-pack. - Compressed responses from an exposed port arrive intact on an install with more than one replica.
- One-hour prompt-cache writes are priced at twice the input rate, instead of the five-minute rate.
- The admin UI's policy and allow-host dialogs match methods and paths as the sandbox proxy does, and no longer warn about access that is kept.
- A path glob with several
**no longer stalls the server. - The sandbox supervisor reaps orphaned processes on kernels such as Kata guests, and those whose name is not UTF-8.
- The cluster proxy stops a Kubernetes watch when its client goes away.
0.34.0 — 26 October 2026#
Sandboxes can be reached with OpenSSH and port forwards, a volume can grow while its sandbox runs, and sandbox pods can request less CPU and memory than their limit. nexusctl remembers an org, a project, and more than one server. Some nexusctl changes break scripts; see Before you upgrade.
SSH. nexusctl sandbox ssh-config prints an OpenSSH entry, so ssh and sftp reach any sandbox in the project. The image needs no sshd. See SSH.
Port forwarding. nexusctl sandbox port-forward forwards a local port to a port on the sandbox's loopback. See Forward a port.
Audit trail. Exec sessions and port forwards are recorded as sandbox.exec and sandbox.port-forward. See What is audited.
Volume growth. An update with a larger volumes[].size grows the volume without a restart. See Persistent volumes.
CPU and memory requests. sandbox.k8s.cpuRequestRatio and sandbox.k8s.memoryRequestRatio let a sandbox pod request less than its limit, so more sandboxes fit on a node. A pod that uses more memory than it requested is evicted first. See Sandbox runtime.
CLI context. nexusctl use <org>/<project> saves the org and project for later commands. nexusctl auth login --server keeps one login for each server. See Context and Log in.
Sandboxes across projects. A sandbox command finds a sandbox by name in every project you can see, and nexusctl sandbox list lists them all when no project is set. See CLI reference.
Integrations. Clusters and AWS connections move to nexusctl integration kubernetes and nexusctl integration aws, and to an Integrations group in the admin UI. See Kubernetes and AWS.
Fixes:
nexusctlstops on a project name that is in more than one organization, instead of using the first match.nexusctlfinds a cluster by name only in the command's project.- A sandbox starts from an image without a CA bundle, such as
ubuntu:24.04, instead of retrying for ever. - Exposed ports no longer grow memory when one side reads slowly.
nexusctl sandbox exec -trestores the terminal when the session ends.- The admin UI disables sandbox actions that a project member who is not an admin cannot do.
- Model pricing was refreshed. Some Claude models were counted at a fraction of list price against spending limits.
- The server image updates body-parser to 2.4.0 and ip-address to 10.7.4, for GHSA-27r3-jxmh-p828 and GHSA-rxp7-6hxx-x8q5.
Before you upgrade
- Remove
--orgfromnexusctl sandbox set-limitandsandbox spend. It now fails. The org comes from the project. - Change
nexusctl clustertonexusctl integration kubernetes, andnexusctl aws-connectiontonexusctl integration aws. There is no alias.get,update,delete, androtate-tunnel-tokenon a cluster now need a project. - Use
<org>/<project>in scripts where a project name is in more than one organization. - Upgrade every
nexusctlthat uses the same~/.nexus/. An oldernexusctlcannot read the credentials file that 0.34.0 writes. Get it withcurl -fsSL https://agents.example.com/install.sh | sh. - Restart running sandboxes before you forward ports to them. Until then, a port forward or
ssh -Lgets503. SSH shells and commands work without a restart.
0.33.1 — 22 October 2026#
Fixes:
- The platform images run Node.js 24.22.1, which fixes the high-severity vulnerabilities in the October 2026 Node.js security release.
0.33.0 — 20 October 2026#
Sandboxes can declare the tools they need, installed before the agent starts through a download cache that fails closed. GitHub App credentials mint short-lived installation tokens, invitations carry project access, and sandboxes and agents get icons.
Sandbox tools. A sandbox's tools lists up to 32 tools as name@version, such as jq@1.7.1, by their mise registry name with no backend prefix. They are installed on every start, before pre-start scripts and the agent, and go first on the PATH of the agent, exec sessions, and scripts, read-only to the agent. Only prebuilt releases install; npm, cargo, pipx, and other backends that build or run code on install are off. A tool that fails to install three times puts the sandbox in error with Tool install failed: and the tool's name. Tools are part of the revision: a change restarts the sandbox and a rollback restores them. Set them through the API, the create_sandbox and update_sandbox MCP tools, a spec file, or the admin UI's YAML view. See Tools.
Tools cache. Tool downloads go through a shared HTTPS cache that the platform deploys into the sandbox namespace the first time a sandbox with tools starts. It allows the hosts mise and common tools download from, such as GitHub, nodejs.org, and go.dev, and serves a stored copy when an upstream is rate-limited or down. A sandbox with tools waits up to a minute for the cache to be ready, then fails to start. sandbox.toolsCache.extraHosts allows more download hosts, *.example.com matching subdomains. With sandbox.toolsCache.enabled: false, each sandbox downloads its tools directly, from any host.
GitHub App credentials. A credential can be a GitHub App: its client ID, private key, installation ID, repositories, and the permissions each token gets. The platform mints installation tokens limited to those repositories and permissions and, by default, injects them into requests to api.github.com and github.com. A policy must grant the credential and allow both hosts. The platform holds the key and tokens outside the sandbox. Creating the credential mints the first token, and a refusal from GitHub names the cause: a wrong key or client ID, an unknown installation, or repositories and permissions outside the installation. Choose Secret: GitHub App in the admin UI's credential dialog, or use the API. Changing the App, key, repositories, or permissions takes a new credential. See Credentials.
Minted sandbox-owned credentials on update. A sandbox update can now add an owned credential that the platform mints, from OAuth client credentials or a GitHub App. To give an existing name a minted source, remove it in one update and add it again in the next, together with its policy.credentials grant. The first token is minted before the update applies; a refusal leaves the sandbox as it was. The admin UI's create and edit sandbox forms offer every source. See Sandbox-owned credentials.
Invitations with project access. An org admin can invite a member with ADMIN or MEMBER on chosen projects, granted when they accept. A pending invitation's role and projects can be edited; changing the role to ADMIN removes the project roles. Accepting keeps any higher role the person already has and skips a project deleted in the meantime. Use the admin UI's invite dialog and pending-invitations table, projectAccess on the invitation API and the client API, or the invite_org_member and new update_org_invitation MCP tools. See Invite people.
Icons. A project admin can give a sandbox an icon from Change icon in its edit dialog, or through the API, as a PNG, JPEG, WebP, GIF, or AVIF up to 10 MiB. The image is cropped to its centre square. Mirantis Agent Platform clients show and upload agent icons through the client API.
Client API.
- A workspace administrator can delete a workspace or project from a Mirantis Agent Platform client, except their own Personal workspace. One that still has agents gets 409.
notify_personnow also tells agents to alert the person when they finish something they worked on over several steps on their own.
Fixes:
- A sandbox whose init container fails goes to
errorwith the reason, instead of staying instarting. - Exec output is held to what the client reads. A command that writes faster than its client reads no longer grows server memory, and a cancel stops output and releases the exec.
- Two updates that add the same sandbox-owned credential name at once get 409 instead of a server error.
- The setup-code command the chart prints ends with a newline, and the setup screen accepts a code pasted with zsh's trailing
%. - Model pricing was refreshed. A model ID that only resellers list is priced at the rate most of them agree on, so one reseller's markup no longer inflates metered cost.
Before you upgrade
- Plan for the tools cache if sandboxes declare tools. On first use the platform creates a PVC of
sandbox.toolsCache.disk(20Giby default) onsandbox.k8s.agentVolumeStorageClass; set the size before then, because the PVC keeps its first size. The cache runs one replica requesting 50m CPU and 64Mi, limited to 1 CPU and 512Mi. It needs HTTPS egress to the download hosts, and sandbox pods need to reach it on port 3128; adjust NetworkPolicies and quotas to allow both. - Grant the new RBAC if you manage it yourself. The chart's sandbox Role now also allows
updateon Secrets,get,create, andupdateon Deployments, andgetandcreateon Services. Withrbac.create: false, add them, or every sandbox with tools fails to start — or setsandbox.toolsCache.enabled: false.
0.32.0 — 15 October 2026#
Every installation now enrolls with Lens Hub, CI runs and other workloads can sign in with their own OIDC token, and sandboxes gain logs, sized volumes, files and pre-start scripts, and image updates.
Hub enrollment. Lens Hub enrollment replaces Lens Cloud activation. Until an installation enrolls, every REST and MCP call outside its setup screen, sign-in, enrollment status, and /health gets 503 fleet_enrollment_required, and no sandbox starts. Connect from the Connect to Lens Hub screen with the setup code the chart writes to <release>-hub-setup, or set hub.fleetId and hub.accessTokenSecret.name. Once enrolled, work continues through Lens Hub outages. nexusctl installation status shows enrollment, /health and the admin UI sidebar show the platform version.
Workload identity federation. An org admin trusts an OIDC issuer — presets for GitHub Actions, GitLab CI, Buildkite, Google Cloud, and Kubernetes — and a project admin creates a federated API token with rules on the workload's claims. The workload exchanges its own token at POST /v1/workload-identity/token for an API token that lasts workloadIdentity.sessionTtlSeconds, an hour by default. Use the Trusted Issuers and Federated Tokens pages, nexusctl workload-identity, or nexusctl federated-token. See Workload identity federation.
Sandboxes.
- Logs. A Logs tab,
nexusctl sandbox logswith-fand--tail, andGET .../sandboxes/{sandboxId}/logsas server-sent events. See Logs. - Volume size.
volumes[].size,--volume /data:5Gi, or the create form set a sandbox's volume size at create.sandbox.k8s.agentVolumeSizeis the default andsandbox.k8s.diskthe ceiling. See Persistent volumes. - Spec fields.
userandworkdirset who the agent runs as and where;filesare written and pre-startscriptsrun before the agent starts. The admin UI edits them too. See Sandbox spec. - Results. A sandbox whose main command exits keeps the result:
completed, orerroron another code, withexitCodeandexitedAt. It stays up forexecandcp, and recovery does not run the command again. See When the main command exits. - Image updates.
imageUpdatefollows the image's tag.{auto: true}rolls a new digest out once the sandbox is idle and goes back if it fails; otherwise take it with Update now,POST .../update-imagewith the digest, orupdate_sandbox_image. Audited assandbox.auto_update. See Image updates.
Access webhooks. accessWebhooks.urls receives a signed access.revoked event within seconds of a person losing access to projects, retried for 24 hours. See Access webhooks.
Client API.
request_website_accesslets an agent ask the person to allow hosts it was refused, andnotify_personlets it alert them.bff.clientMcp.intentLifetimeSecondssets how long a person has to act on an agent's request, one day by default, up from a fixed 15 minutes.- Push notifications to the Mirantis Agent Platform iOS app, through Lens Hub, are off by default.
- Prism Agent sandboxes created from a Mirantis Agent Platform client on AWS Bedrock default to Claude Haiku 5.5.
Admin UI. Organizations and projects have a Settings page for org admins. The org overview charts the average cost per 1M tokens, counting input, output, and cache tokens.
Fixes:
- A change to a sandbox's policies reaches it, and the forward proxy, on every replica within seconds. Before, the sandbox could keep the old policy for up to 10 minutes, and the forward proxy for up to 5.
- Deleting a project or organization that still has sandboxes is refused with 409, with a message saying how many to delete first.
- The admin UI renews an expired session with its refresh token instead of asking you to sign in again.
- Servers that speak first, such as SSH, work through a cluster tunnel.
- MCP agents see the descriptions of credential fields.
Before you upgrade
- Plan time to enroll. An installation activated against Lens Cloud forgets that activation on the upgrade, and everyone signs in once more. Users, organizations, projects, and data stay. No agent work runs, and no sandbox starts or recovers, until it has enrolled with Lens Hub. Upgrade with
--reset-then-reuse-values;--reuse-valueskeeps the old chart's defaults and fails on the newhubvalues. - Set
oidc.useExternalProvider=trueif you sign in through your own identity provider, withoidc.clientId, before the installation enrolls. Without it, the installation enrolls in Lens ID mode. See SSO. - List delegated clients for the client gate. With
oidc.clientIdandoidc.directAccessRoleempty,oidc.clientGate(OIDC_CLIENT_GATE, defaultauto) answers401to a token issued to any client other than the installation's own or one inoidc.delegatedClients(OIDC_DELEGATED_CLIENTS). With the client API, addbff.tokenExchange.clientIdthere, or withbff.nexusAuth=forwardthe clients inbff.oidc.allowedAzp, or setoidc.clientGate: "never". The install fails otherwise. See Token clients without a role. - Drop
activation.apiUrlandactivation.bootstrapClientIdfrom your values; they are no longer read.nexusctl installation activateand the/v1/installation/activationroutes are removed. - A sandbox whose main command exits no longer starts again. It stays
completedorerror. Prism Agent sandboxes that runprism-agent:latestwithEXIT_ON_UPDATE=1change toimageUpdate: {auto: true}, andEXIT_ON_UPDATEleaves their revisions, with no record in the revision history. A running one keeps the variable until its next start, so the first new digest can still end it ascompleted; start it again. New Prism Agent sandboxes getimageUpdate: {auto: true}in place ofEXIT_ON_UPDATE. - Upgrade the chart for sandbox logs. It grants the platform
getonpods/log.
0.31.1 — 13 October 2026#
Fixes:
- The server image now includes the
nexusctlbinaries./install.shinstalls the CLI. See Set up the CLI.
0.31.0 — 8 October 2026#
Teams are replaced by project roles given straight to people and API tokens, idle sandboxes can stop and delete themselves, and the forward proxy holds every CONNECT to the sandbox's policy.
Project members. An org admin gives an org member or API token ADMIN or MEMBER on a project from the new Members page, nexusctl project member set, /v1/projects/{projectId}/members, or the set_project_member MCP tool. Changes are audited as project-member. See Project members.
Sandbox timers. --auto-stop 30m stops an idle sandbox, --auto-delete 1d deletes a stopped one with its volume, and --auto-start starts an auto-stopped sandbox again on the next exec, terminal, or private-port request. Set them on create, in a spec file, or in the UI, and change them with nexusctl sandbox update without a restart. Timers are opt-in. See Stop and delete idle sandboxes.
Sandbox restart. POST /v1/projects/{projectId}/sandboxes/{sandboxId}/restart or the restart_sandbox MCP tool re-provisions the active revision, or starts a stopped sandbox. See Restart.
Policy drift shows what the org ceiling removed. drift.narrowedDomains, drift.blockedDomainDetails, and the sandbox Policy tab. See Policy bindings.
Exposed ports. sandboxIngress.corsOrigins lets browser apps on other origins call private ports with a bearer token. The session cookie now counts only on requests from the sandbox's own private-port origins. Public ports now receive the Authorization header. See Exposed ports.
Install and inference.
config.maxHeaderBytessets the largest request header block, default32768.- A policy with no provider gets Bedrock where available, otherwise the first backend the install serves with its own key.
GET /v1/inference/providersreports it asdefaultProvider. - OAuth catalog entries take an optional
manageAccessUrl. See OAuth applications. - The client API can serve an agent-facing MCP at
/mcp/client(bff.clientMcp.url) and forward each person's own token withbff.nexusAuth=forward.
Fixes:
- GitHub connector sign-ins and refreshes work.
- Claude Code and Codex finish signing in instead of failing with an issuer mismatch.
- Multi-replica installs behave as one: MCP sessions and cluster tunnels work across replicas.
- Re-applying an unchanged spec no longer restarts a sandbox.
- A sandbox in
errorstarts recovering at once. - Public port hostnames stay reachable after the sandbox's data tunnel drops.
- Status 204, 205, and 304 responses pass through instead of becoming 502.
- Model pricing was refreshed. Claude Haiku 5.5 is priced.
Before you upgrade
- Back up the database. The upgrade converts teams to project roles and drops them, irreversibly. Each principal keeps its highest role per project.
- Rebind cluster RBAC. Users and API tokens now arrive with
<org>/<project>and<org>/<project>:adminor:memberin place of<org>/<team>. A binding on<org>/<project>now also covers everyone with a role on that project. - Move scripts off team surfaces.
nexusctl team, the team routes and MCP tools, and the Teams pages are removed. - Allow
<public URL>/oauth/callbackon anoidc.clientIdyou provisioned yourself. Loopback sign-ins, such as Claude Code and Codex, now use it with PKCES256. - Check forward-proxy traffic. A
CONNECTto a host the policy does not routeupstreamis now refused with 403 and audited. Add hosts agents still need to their policy. - Bedrock without a token is offered only when the AWS credential chain finds credentials at boot. Override with
inference.bedrock.ambientCredentials. See AWS Bedrock.
0.30.0 — 2 October 2026#
Organizations can bring their own inference keys, the API can require a realm role, and the project shell sandbox is replaced by agent sandboxes.
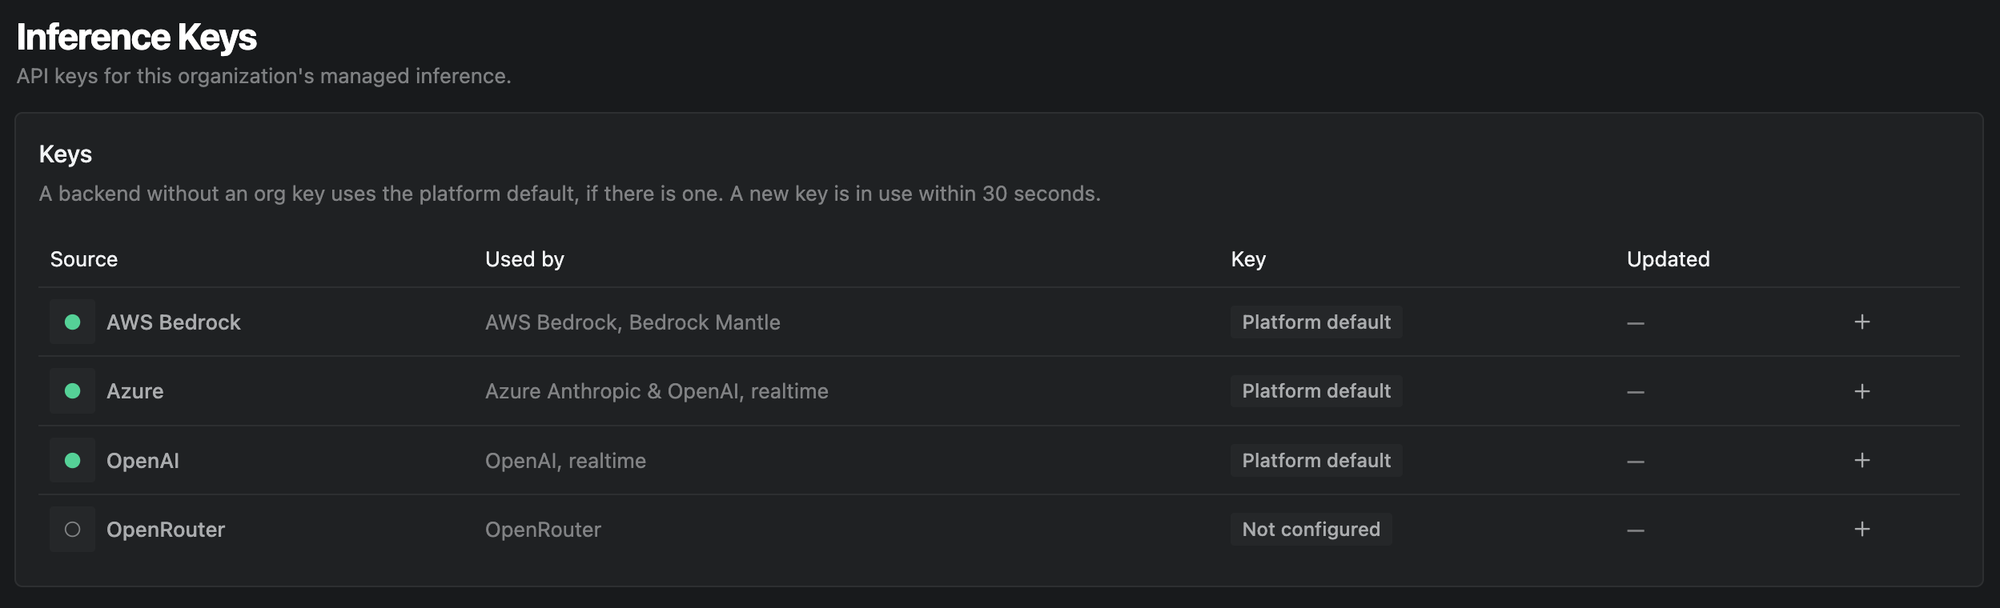
Org inference keys. An org admin sets the org's own key for a backend on the new Inference Keys page or with PUT /v1/orgs/{orgId}/inference/keys/{source}. The org's key takes priority over the install's. Every deployment token is now optional; inference.deploymentKeyFallback (default true) decides whether organizations without a key use the install's. See Inference providers.
Direct-access gate. With oidc.directAccessRole set, only people with that realm role can use the admin UI, nexusctl, the REST API, or an MCP client directly. It is off by default; roll it out with oidc.directAccessReportOnly: true first. See SSO.
Client API subchart. bff.enabled=true installs the Mirantis Agent Platform client API on its own public host, with per-person token exchange (Keycloak 26.2 or later).
OAuth and credentials.
config.upstreamOAuthAdditionalRedirectUrislists extra redirect URIs a project admin can allow on an OAuth Login credential. See Allow extra redirect URIs.- A credential can hold an OAuth client (OAuth client credentials); the platform mints and renews the token outside the sandbox. See Credentials.
- Prism Agent connects to Microsoft Teams.
CLI. nexusctl sandbox run runs one command in a new sandbox (--rm deletes it afterwards), and nexusctl sandbox cp copies files to and from a sandbox. See CLI reference.
GPT-Live voice sessions are proxied for policies that grant openai or azure, like Realtime.
Fixes:
- Google connections stay signed in when the shared OAuth application sets
"accessType": "offline"and"prompt": "consent". - The forward proxy refuses internal targets: loopback, link-local (cloud metadata included), and the server's own address.
- One admin UI session across tabs.
- New Hermes Agent and OpenClaw sandboxes default to Claude Opus 5.5, except on LiteLLM.
- Model pricing was refreshed. Claude Sonnet 5.5 and the GPT-6.1 Sol family are priced.
Before you upgrade
- Pin a model. The platform no longer sets
ANTHROPIC_MODELin sandboxes, and theinference.*.modelHelm values are removed. SetANTHROPIC_MODELin the policyenv. - Recreate Hermes Agent sandboxes created before 0.30.0, or set
LENS_MANAGED_INFERENCE_MODELin the policyenvuntil you do. -
Move off the shell sandbox.
nexusctl shell exec,POST /v1/shell/exec, the shell-session endpoints, and theshell_*MCP tools are removed. Usenexusctl sandbox run --rmorsandbox exec, and dropsandbox.image,sandbox.k8s.workspaceStorageClass, andsandbox.k8s.activeDeadlineSecondsfrom your values. Delete the old shell workspaces when you no longer need them:kubectl get pvc -n <sandbox-namespace> -o name | grep '/sandbox-workspace-' | xargs kubectl delete -n <sandbox-namespace> -
Verify owner emails. An address in
config.ownerEmailsis refused when its token saysemail_verified: false. /oauth/tokenrelays only interactive grants:authorization_code,refresh_token, and the device-code grant. Others get 400.
0.29.0 — 28 September 2026#
Your own LiteLLM proxy as a managed-inference backend, and OAuth applications configured once for the whole install.
LiteLLM backend. Point the install at your LiteLLM proxy with inference.litellm.baseUrl and a token, and select it in a policy with provider: litellm. Sandboxes get both wire formats. Spend is the cost LiteLLM reports; a call with no reported cost counts zero against spending limits, so price every model in LiteLLM and set include_cost_in_streaming_usage. inference.litellm.forwardTags=true tags each call with its project. See Inference providers.
Microsoft Foundry serves Realtime voice sessions for policies that grant azure. See Realtime voice sessions.
OAuth Login applications for every organization. An operator stores a JSON catalog of OAuth clients in a Secret (oauthApplications.existingSecret), and project admins pick an application in a connector's Authentication dropdown. The catalog is read at startup; restart every replica after an edit. See MCP connectors.
agent-sandbox runtime. sandbox.provisioner=kubernetes-agent-sandbox runs each sandbox as a kubernetes-sigs/agent-sandbox Sandbox. Install the controller first, and stop every sandbox before you switch. See Sandbox runtime.
Private ports identify the caller with x-forwarded-user-id and x-forwarded-user-display-name (percent-encoded).
ADDRESS is a PII masking type again. Re-add it to policies that should mask street addresses.
Fixes:
- A saved OAuth scope can be cleared with
"scope": null. - OAuth Login forms are consistent across the connector and credential dialogs.
- The Prism Agent template uses Microsoft Foundry as the voice backend and sets
EXIT_ON_UPDATE=1. - Model pricing was refreshed. Claude Opus 5.5 and the GPT-6 Luna and Sol families are priced.
0.28.0 — 16 September 2026#
A sandbox can hold more than one inference backend, and admins can read and repair header formats.
Multiple inference backends per sandbox. A policy names a primary in managedInference.provider and every enabled backend in managedInference.providers. Each backend gets its own endpoint and placeholder credential under LENS_INFERENCE_<PROVIDER>_*, and all are metered against the same spending limits. The agent chooses between them; restart a running agent after you change its providers. The admin UI authors the list from the sandbox template. See Inference providers.
Project admins can read header formats in their own project, so a format masked as [REDACTED] can be inspected and rotated. See Injection.
Header formats accept Basic-auth literals. {base64:<prefix>{value}} and the usernames x-access-token, oauth2, and x-token-auth let one GitHub PAT serve both api.github.com and git-over-HTTPS.
MCP connector OAuth providers are discovered from RFC 9728 protected-resource metadata, falling back to origin discovery. When a provider changes its issuer or resource, create a new authorization-code credential and move the connector's policies to it.
Deleting a project keeps its audit and billing history, so organization totals do not change. Deleting an organization still erases its history. See Audit trail.
Fixes:
- A healthy sandbox is no longer failed for landing on another replica.
- A blocked project or organization delete answers 409 naming what to remove, instead of 500. Repoint automation that retried the 500.
- A stopped sandbox's spec can be corrected, and a new revision can be promoted straight to active.
- Provisioning claims survive a lost replica.
- Slack calls from a template authenticate. An injection can name a urlencoded body field.
- Credential dialog corrections.
- Model pricing was refreshed.
0.27.0 — 3 September 2026#
Project and organization overview. Counts of sandboxes, policies, and credentials, 30-day inference spend, and daily spend by sandbox, model, or provider.
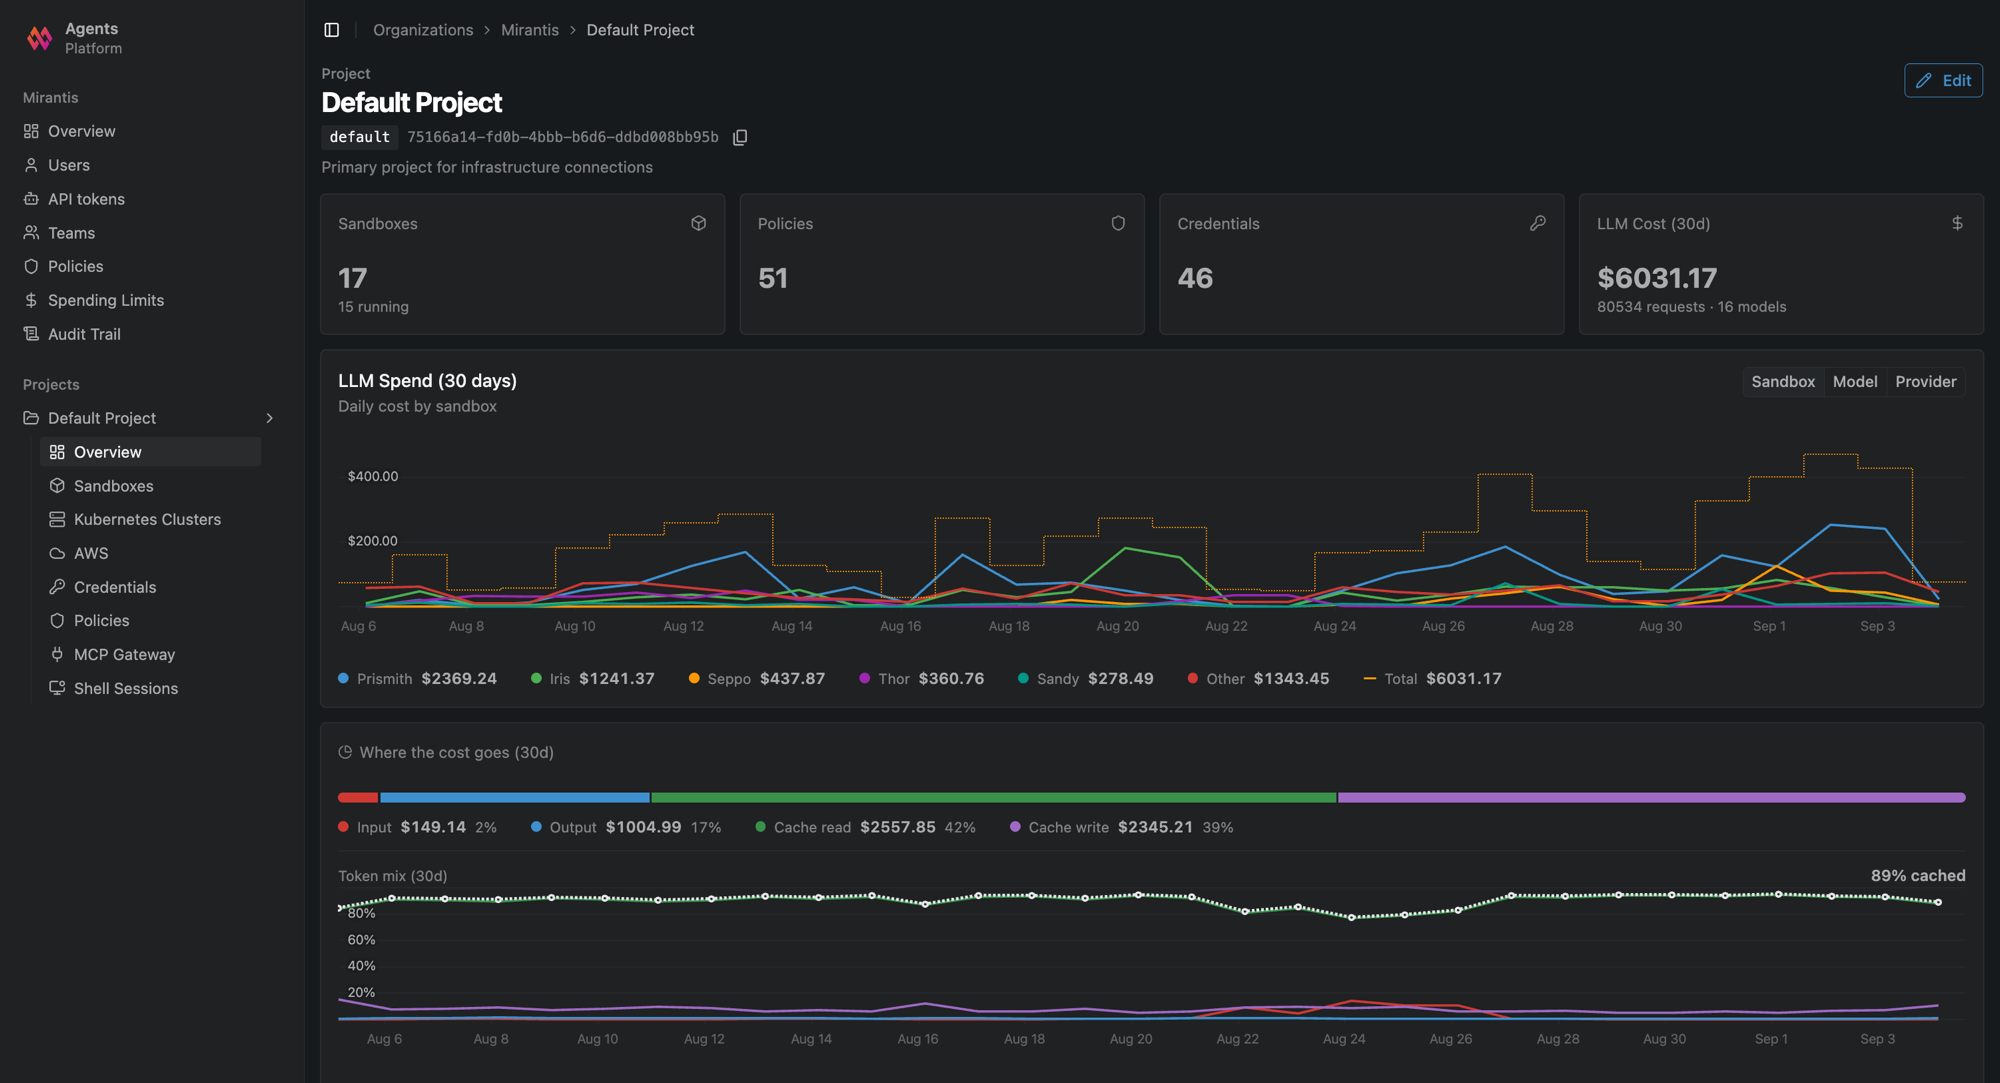
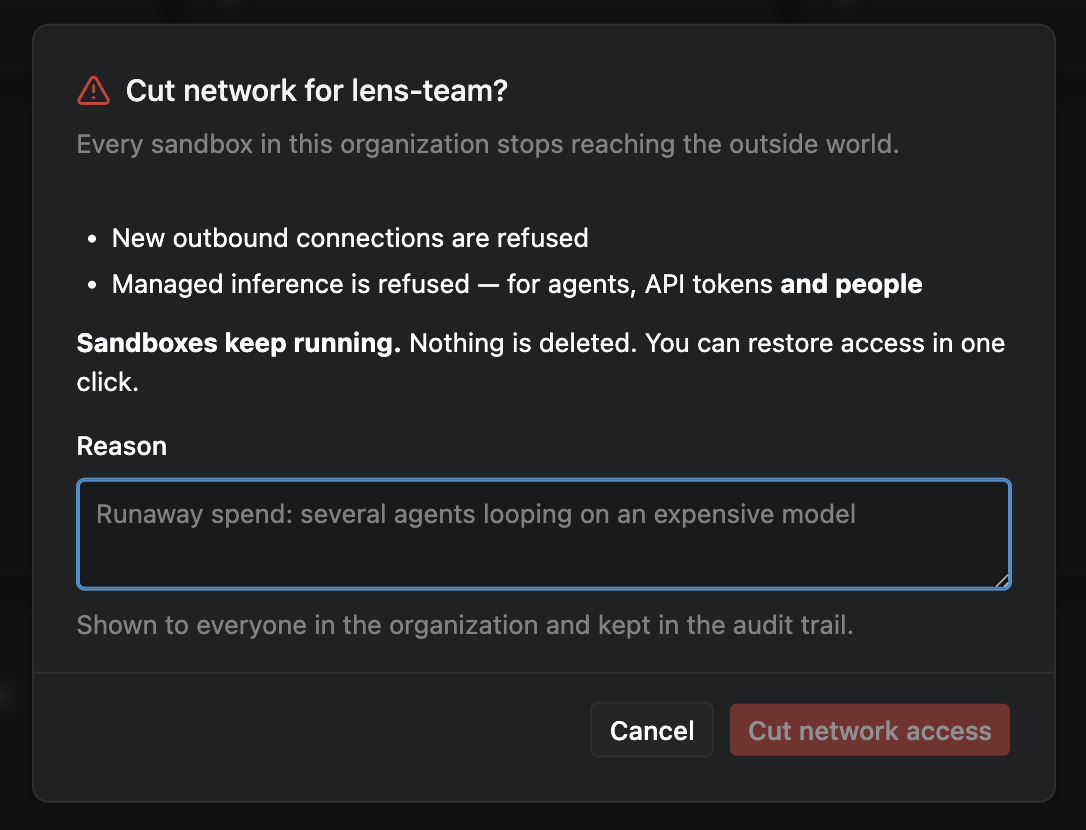
Emergency halt. Cut network access stops managed inference, connector calls, both proxies, and Kubernetes exec, attach, and port-forward for a whole organization, and pushes a deny-all policy to every sandbox. Sandboxes keep running. Admin UI and REST API only. See Emergency halt.
Up to four exposed ports per sandbox, each with its own auth. Sandboxes created before the upgrade serve one port until they restart. See Exposed ports.
Requests arrive with the browser's own Host header.
Spending limits can name a project. Org and project limits are set by an org admin; a project admin can cap a sandbox. See Spending limits.
GraphQL policy rules can bound arguments with a JSON pointer and a glob. See Binding a GraphQL operation to a subject.
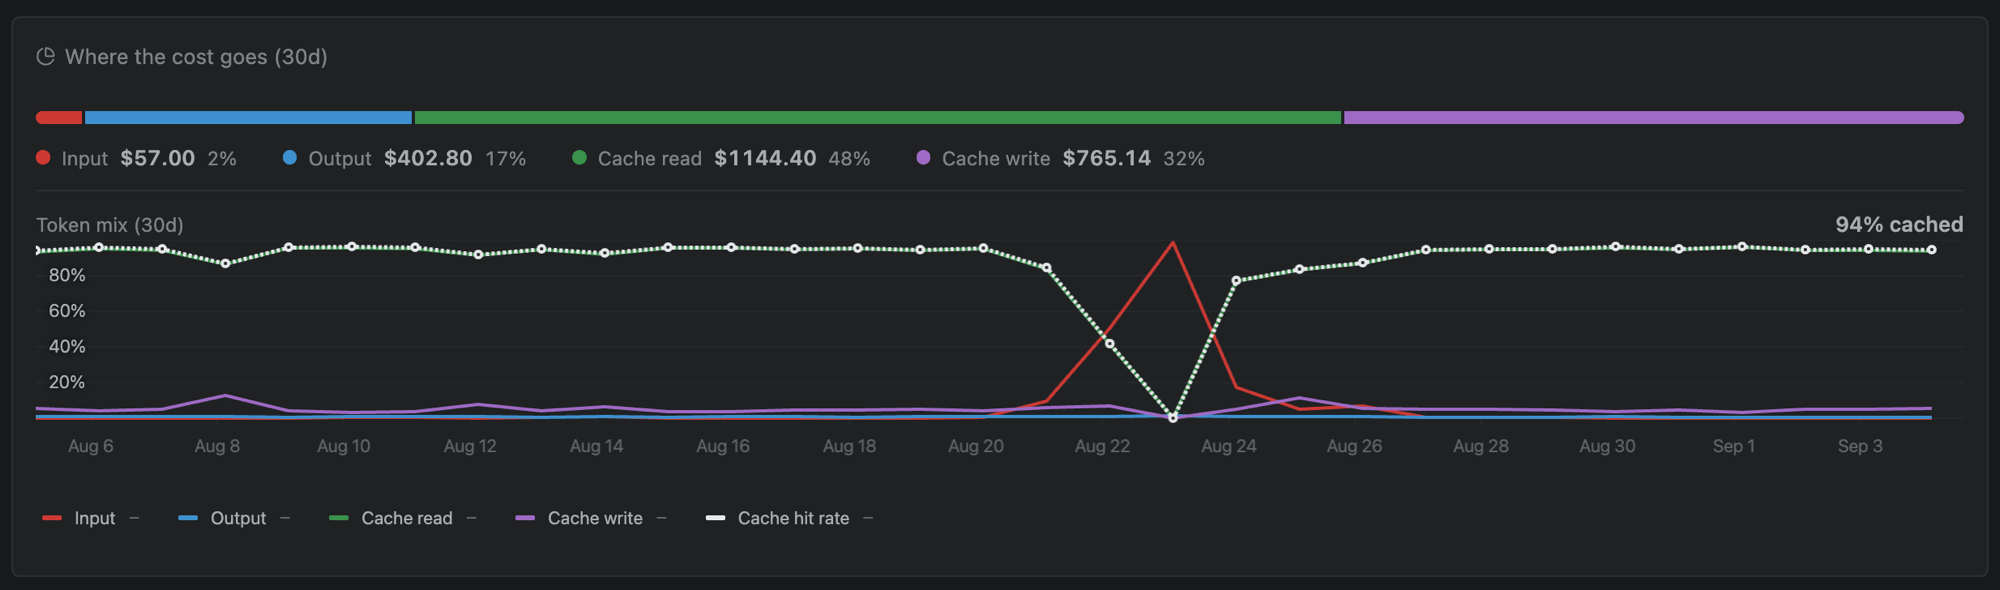
Prompt cache costs appear on the cost card, with a cache hit rate.
OpenClaw is a built-in sandbox template (2026.8.2). Hermes Agent moved to v2026.8.19.
Fixes:
- A credential and its header injection are written together.
- OAuth client-credentials tokens are renewed before they expire.
- Metered spend is attributed to the project's organization.
- Five policy-resolution fixes. Re-run
policy-binding list-driftafter upgrading. - The audit trail attributes a request through several proxies to the original caller.
- Audit-trail queries accept
excludeReads=true. - MCP session recovery,
tools/list_changed, and stdio fixes, and admin UI fixes. - Model pricing was refreshed.
Cost attribution changes in this release
Spend that was attributed to no organization now counts toward org totals and spending limits, and some rates moved. Review org-level limits before upgrading.
0.26.0 — 25 August 2026#
OpenRouter backend. Set inference.openrouter.token and a policy can select openrouter: one key for many vendors' models, served in both the Anthropic and OpenAI wire formats. It is billed on the cost OpenRouter reports. See Inference providers.
Agents are told which backend they were given in LENS_MANAGED_INFERENCE_PROVIDER and LENS_MANAGED_INFERENCE_MODEL.
Unmetered spend is flagged. A sandbox that calls a provider directly, outside managed inference, shows a card naming the hosts, because that spend escapes its spending limit.
Policies can scope a route by caller binary and by GraphQL operation, with binaries on a domain and graphql on an HTTP rule. Org ceilings only narrow them.
The CLI installs from your own server. curl -fsSL https://agents.example.com/install.sh | sh installs a matching nexusctl. See Set up the CLI.
Installation owners. config.ownerEmails limits who may create organizations; other people are admitted only with an org or an invitation. See SSO.
Fixes:
- A truncated stream is recorded as an error (
streamTruncated) in the audit trail, and the response fails. - Pricing corrections: model variant suffixes and Bedrock cross-region profile ids are priced.
- A partial policy edit merges instead of replacing the embedded policy.
- Four policy-fence corrections. A binary must be an absolute path.
- Credentials survive a rolling deploy, and OAuth consents carry over to credentials.
- MCP tool names stay within 64 characters.
- Admin UI: stop works from
creatingandstarting.
Cost accounting changes in this release
OpenRouter is billed on its reported cost, models missing from the rate card now count toward caps, and some rates moved. Review spending limits before upgrading.
0.25.0 — 17 August 2026#
Allow or deny a blocked host from the blocked-requests card, without opening the policy editor.
The sandbox detail page is redesigned.
Fixes:
- Bedrock traffic is priced and attributed as Bedrock.
- Bedrock embeddings and other non-Anthropic shapes are metered instead of recording zero.
- Model pricing was resynced.
claude-3.5-sonnetandclaude-3-sonnetnow have no price. - A dropped deny entry no longer reads as drift in
policy-binding list-drift. - The ingress data tunnel retries indefinitely, so a sandbox reconnects after a long outage.
Cost accounting changes in this release
Recorded Bedrock cost rises toward your real invoice. Review spending limits before upgrading, and repoint anything pinned to claude-3.5-sonnet or claude-3-sonnet, because unpriced traffic does not count toward limits.
0.24.0 — 12 August 2026#
OpenAI Realtime voice sessions run through managed inference over a WebSocket, with audit per response. PII masking does not run on them (piiMaskingSkipped), the spending limit is checked per response, and each project can hold eight concurrent sessions per replica.
Fixes:
- Cached OpenAI tokens are no longer billed twice, and audio is metered.
- First-party model prices take precedence over aggregator entries, so realtime audio is priced at OpenAI's rate.
If you run OpenAI workloads
Cached-token cost drops and realtime and audio cost rises. Review spending limits before upgrading.
0.23.0 — 12 August 2026#
OpenAI backend. Select openai as a managed-inference provider with an OpenAI API key; it serves GPT only. inference.openai.baseUrl points it at any OpenAI-compatible https endpoint. Only chat completions, responses, and embeddings are proxied, because other paths are not metered.
Fixes:
- PII masking skips multipart uploads, recorded as
piiMaskingSkippedin the audit trail. - Model pricing was refreshed.
0.22.0 — 11 August 2026#
Sandboxes record what they were given. Each sandbox keeps a record of the policies, credentials, and configuration it was provisioned with, so an investigation can answer "what did this agent actually have" without reconstructing it from history.
Fixes:
- Model pricing refreshed, so usage costs and spending limits reflect what you are really being billed.
- Admin UI. The sandbox list answers common questions inline, and breadcrumbs are built from the URL rather than guessed from name fragments — so deep links and names containing slashes behave.
0.21.0 — 10 August 2026#
Sandbox-owned policies and credentials. A sandbox can carry its own embedded policy and credentials, created and deleted with it.
Sandboxes as YAML. nexusctl sandbox create -f sandbox.yaml, and YAML authoring in the admin UI for sandboxes and policies.
Effective policy view. See what a sandbox's merged, ceiling-clipped policy resolves to.
PII masking is substantially faster.
Fixes:
- Connector credential handling hardened. A header format with an inline secret is masked.
If you use connectors with header credentials
Header formats that contained a secret inline are converted on upgrade. Review your connector credentials afterwards.
0.20.1 — 31 July 2026#
Org ceilings intersect HTTP rules. Where an org policy and a project policy both carry HTTP method and path rules, the effective rules are now the intersection rather than the union. This is a correctness fix with real consequences: a project can no longer widen the org ceiling's HTTP rules by adding its own.
Review policy-binding list-drift after upgrading. Projects that were unintentionally relying on the previous behaviour will show as clipped.
Masked PII is restored in tool-call arguments, so an agent receives usable values back from a masked round trip.
Database sessions are pinned to UTC, which fixes charts and time-bucketed queries drifting for installs in non-UTC regions.
0.20.0 — 30 July 2026#
PII masking fails closed, properly. A dead masking worker now returns 503 rather than forwarding unmasked content, and it does so even when the policy sets failOpen. An infrastructure failure is not a licence to leak.
Exec across replicas. Sandbox exec and terminal sessions route correctly on multi-replica installs, so interactive sessions no longer depend on reaching the right pod.
0.19.1 – 0.19.3 — 27–29 July 2026#
Stability and isolation fixes.
- Credential domains no longer grant egress. Attaching a credential for a domain no longer implicitly allows the sandbox to reach it. A policy must allow the domain explicitly. Check your policies after upgrading — an agent that relied on the implicit grant will start being denied.
- Sandbox principals get a real Kubernetes impersonation identity, so cluster-side audit names the agent.
- Idle-connection and job-queue errors no longer crash the process.
- The cluster relay forwards real upstream
101headers, fixing protocol upgrades over the tunnel.
0.19.0 — 22 July 2026#
Agents can read their own spend. A sandbox identity can query its own spending status and usage over MCP, scoped to itself. A well-behaved agent can wind down before it hits its cap rather than being cut off mid-task.
Sandbox cost and limit reads are force-scoped to the calling sandbox, and a malformed sandbox context is denied instead of falling back to an org-wide read.
0.18.0 — 22 July 2026#
Per-sandbox CPU and memory, with a ceiling. Every sandbox declares its own resources, bounded by an install-wide ceiling. A request above the ceiling is rejected rather than silently clipped, and the ceiling is validated at startup.
Breaking change
cpu and memory are now required on sandbox creation. Update any automation that creates sandboxes without them. Set the install ceilings with sandbox.k8s.cpu and sandbox.k8s.memory. See Install on Kubernetes.
Project admins can manage project-scoped resources, and API tokens with project admin get the full sandbox tool set over MCP.
Connector credentials are selectable inline on a policy's connector row in the admin UI.
0.17.0 — 17 July 2026#
Chiefly a PII masking release, and a substantial one.
Masking covers far more of a request. The top-level system prompt, tool-call arguments in chat history, document title and context, refusal and JSON tool-result content, and array-shaped function-call output are all masked now. Structural metadata is deliberately left alone, so masking no longer breaks request shapes.
Long inputs are handled honestly. Named-entity recognition runs over a sliding window with a bounded budget, and coverage truncation is reported per call rather than passing silently. Over-budget fields are truncated to keep masking complete.
Signed thinking content is never rehydrated on the response side.
Sandbox tokens are pinned to their project, closing a cross-project access path.
0.16.0 – 0.16.1 — 10–13 July 2026#
Bedrock Mantle is available as a managed-inference backend, serving both Claude and GPT off the same Bedrock key. It appears automatically when a Bedrock token is configured.
PII propagation is faster and safer. The propagation sweep is a single-pass Aho-Corasick scan with bounded memory, deterministic results, and fail-closed behaviour on long text.
0.15.0 — 9 July 2026#
Response-streaming correctness for exposed ports and the cluster tunnel: chunked responses are dechunked correctly, hop-by-hop framing headers are stripped, stale Content-Length headers are dropped, and ingress streaming has backpressure and an idle deadline.
If an agent's web UI behaved oddly behind the sandbox ingress before, this release is the fix.
0.14.0 — 8 July 2026#
Microsoft Foundry managed inference. Claude on the Anthropic Messages API and GPT on both Chat Completions and the Responses API, from one Foundry resource and key. Streaming usage is metered, so spending limits apply to streamed responses too.
The proxy enforces the policy's provider selection at the boundary: a policy naming a provider the install has not configured is refused rather than quietly falling back. See Inference providers.
0.13.0 — 7 July 2026#
The symmetric org and project policy model. This is the release that introduced org policies as a ceiling rather than a default, with a sandbox policy-clip report and an effective-policy readout so clipping is visible instead of mysterious.
Connector tools inside agent sandboxes. A project's connectors are exposed as MCP tools within agent sandboxes, so an agent reaches them the same way whether it runs inside the platform or connects from outside.
The audit trail resolves sandbox names and surfaces PII masking status, so entries read as something other than a wall of identifiers.
0.12.0 — 2 July 2026#
On-prem activation. The device-flow activation, replaced by Hub enrollment in 0.32.0, shipped in the chart, along with air-gapped license-file activation for installs that must never reach Lens Cloud. activation.apiUrl defaults to production Lens Cloud.
Sandbox templates for well-known agents, and egress policy templates for common domains, so a first agent does not start from an empty form.
Per-sandbox spend and spending limits are visible in the admin UI.
Earlier releases#
Versions 0.7.0 through 0.11.0 (May and June 2026) built out identity, RBAC, the audit trail, connectors, and the sandbox runtime ahead of the on-prem chart.
Upgrading#
- Read the notes for every version between yours and the target, not only the newest — the breaking changes above are cumulative.
- Back up the database.
helm upgrade lens-agents oci://ghcr.io/lensapp/lens-agents --reset-then-reuse-values --wait- Run
nexusctl policy-binding list-drift --org <org>afterwards. Policy-resolution fixes are the changes most likely to alter what your agents can reach.
Planning an upgrade across several versions, or running an air-gapped install? Talk to us.