Run OpenClaw as a personal assistant on Mirantis Agent Platform#
OpenClaw is a personal AI assistant with a web Control UI. On an open port, anyone who finds that UI can talk to your assistant. In a Mirantis Agent Platform sandbox, the Control UI has no open port: it is a private port behind your platform login, and OpenClaw knows who you are from the platform. The model comes through managed inference with OpenRouter, so the sandbox holds no API key, and you decide what else on the network the assistant can reach.
OpenClaw is useful because it acts for you: it remembers, it runs tools, and it does things. An assistant with your context and your keys on an open port acts the same way for anyone who finds it. This tutorial runs OpenClaw for one person, with none of that exposed.
How the pieces fit#
OpenClaw runs a gateway that serves the Control UI and talks to the model. In the sandbox, the gateway listens only on 127.0.0.1. The sandbox publishes that port as private: the platform gives the port a URL, asks you to log in, checks your project access, and then forwards the request with your identity in a header. OpenClaw trusts that header, so it knows who you are without a second password. Exposed ports describes private ports.
The model comes through managed inference. The sandbox gets an OpenRouter endpoint and a placeholder key. The platform adds the real key at its boundary and meters the spend. OpenRouter is the easiest backend to set up: one API key, no cloud account, and hundreds of models behind it. Models describes managed inference.
What you need#
- A current Mirantis Agent Platform release, with OpenRouter enabled for your organization. An org admin adds the OpenRouter API key on the organization's Inference keys page. If you don't have a platform yet, see Getting started.
nexusctl, installed from your platform and logged in withnexusctl auth login. See Set up the CLI.- The email address that you log in to the platform with. OpenClaw makes that identity the admin of the gateway.
Step 1: Define the sandbox#
Save the following spec as sandbox.yaml. Sandbox spec describes every field.
name: OpenClaw
image: ghcr.io/openclaw/openclaw:2026.10.8
cpu: "2"
memory: 4Gi

volumes:
  - mountPath: /data
    size: 10Gi

exposedPorts:
  - name: web
    port: 18789
    auth: private

env:
  LENS_SANDBOX_WRITABLE_DIR: /data
  OPENCLAW_CONFIG_PATH: /data/openclaw.json
  OPENCLAW_STATE_DIR: /data/state
  OPENCLAW_WORKSPACE_DIR: /data/workspace
  OPENCLAW_NO_AUTO_UPDATE: "1"
  OPENCLAW_MODEL: anthropic/claude-opus-5.5
  OPENCLAW_ADMIN: ${OPENCLAW_ADMIN}

files:
  - path: /home/node/start-openclaw.sh
    content: |
      [ -n "$NEXUS_INGRESS_IDENTITY_HEADER_WEB" ] || { echo "publish the web port as private" >&2; exit 1; }
      origins="\"$(printf '%s' "$NEXUS_INGRESS_ORIGINS_WEB" | sed 's/,/","/g')\""

      openclaw config unset gateway.auth.identityScopes >/dev/null 2>&1
      openclaw config set gateway "{
        \"mode\": \"local\", \"bind\": \"loopback\", \"port\": 18789,
        \"trustedProxies\": [\"127.0.0.1\"],
        \"auth\": {
          \"mode\": \"trusted-proxy\",
          \"trustedProxy\": {
            \"userHeader\": \"$NEXUS_INGRESS_IDENTITY_HEADER_WEB\", \"allowLoopback\": true,
            \"deviceAutoApprove\": {
              \"enabled\": true,
              \"scopes\": [\"operator.read\", \"operator.write\", \"operator.approvals\", \"operator.questions\"]
            }
          },
          \"identityScopes\": { \"$OPENCLAW_ADMIN\": [\"operator.admin\"] }
        },
        \"controlUi\": {
          \"allowedOrigins\": [$origins],
          \"dangerouslyAllowHostHeaderOriginFallback\": false,
          \"dangerouslyDisableDeviceAuth\": true
        }
      }" --strict-json --merge || exit 1

      openclaw config set update '{"checkOnStart": false, "auto": {"enabled": false}}' --strict-json --merge

      openclaw config set models.providers.nexus "{
        \"api\": \"anthropic-messages\",
        \"baseUrl\": \"$ANTHROPIC_BASE_URL\",
        \"apiKey\": \"nexus-managed\",
        \"models\": [{\"id\": \"$OPENCLAW_MODEL\", \"name\": \"$OPENCLAW_MODEL\"}]
      }" --strict-json
      openclaw config set agents.defaults.model "{\"primary\": \"nexus/$OPENCLAW_MODEL\"}" --strict-json --merge
      openclaw config set memory.search "{
        \"enabled\": true, \"provider\": \"openai\",
        \"model\": \"openai/text-embedding-3-small\", \"fallback\": \"none\",
        \"remote\": { \"baseUrl\": \"$OPENAI_BASE_URL\", \"apiKey\": \"$OPENAI_API_KEY\" }
      }" --strict-json --merge

      openclaw config set mcp.servers.nexus "{
        \"command\": \"/.lens/nexus-mcp\", \"enabled\": true,
        \"env\": {
          \"NEXUS_MCP_URL\": \"$NEXUS_MCP_URL\",
          \"HTTPS_PROXY\": \"$HTTPS_PROXY\",
          \"HTTP_PROXY\": \"$HTTP_PROXY\",
          \"SSL_CERT_FILE\": \"$SSL_CERT_FILE\"
        }
      }" --strict-json

      exec openclaw gateway

command: sh /home/node/start-openclaw.sh

policy:
  name: OpenClaw
  networkDefaultVerdict: deny
  managedInference:
    enabled: true
    provider: openrouter
  allowedDomains:
    - pattern: "*"
      verdict: allow
      transport: direct
      description: Read-only internet
      rules:
        - { method: GET }
        - { method: HEAD }
Some details of this spec matter for OpenClaw:
- The image is pinned, and
OPENCLAW_NO_AUTO_UPDATEtogether with theupdatesetting keep it pinned. An assistant that upgrades itself is no longer the one you reviewed. - State lives on the
/datavolume: config, memory, and workspace. After a restart, the assistant continues where it left off.LENS_SANDBOX_WRITABLE_DIRgives the volume to the image's own user before the gateway starts. - The start script writes OpenClaw's settings on every boot with OpenClaw's own
config set, then starts the gateway. Settings that you change in the Control UI stay, except the ones the script owns. - The gateway trusts only the platform. It binds to loopback and reads your identity from the header that the private port adds. The allowed origins are the URLs of this sandbox, so another site can't drive the Control UI from your browser.
- Only you administer it.
OPENCLAW_ADMINgets the admin scope: channels, devices, and gateway settings. Anyone else in the project who opens the port can chat and answer approvals, but can't change the gateway. - You decide what the assistant can reach. The policy denies by default. OpenClaw talks to the model through managed inference, which the policy grants separately. The one rule in
allowedDomainsgives read-only internet:GETandHEADpass, so the assistant can read the web but can't post to it. The same rule lets OpenClaw read its model catalog and download skills from ClawHub. Remove the rule to block all of that, or add domains with the methods you trust. - Memory search uses OpenRouter too. OpenClaw indexes its memory with an embedding model, and the script points it at the same managed OpenRouter endpoint, through OpenRouter's OpenAI-compatible API.
OPENCLAW_MODELis any OpenRouter model ID. Change it to try another model.
Step 2: Create the sandbox#
Create the sandbox from the spec. Replace you@example.com with the email address you log in to the platform with, and <org>/<project> with your organization and project.
OPENCLAW_ADMIN=you@example.com nexusctl sandbox create --project <org>/<project> -f sandbox.yaml
create expands ${OPENCLAW_ADMIN} from your environment. The image is large, so the first start takes a few minutes.
Step 3: Open the Control UI#
Find the URL of the sandbox's private port. Replace <sandbox> with the sandbox's name.
nexusctl sandbox describe <sandbox> --project <org>/<project>
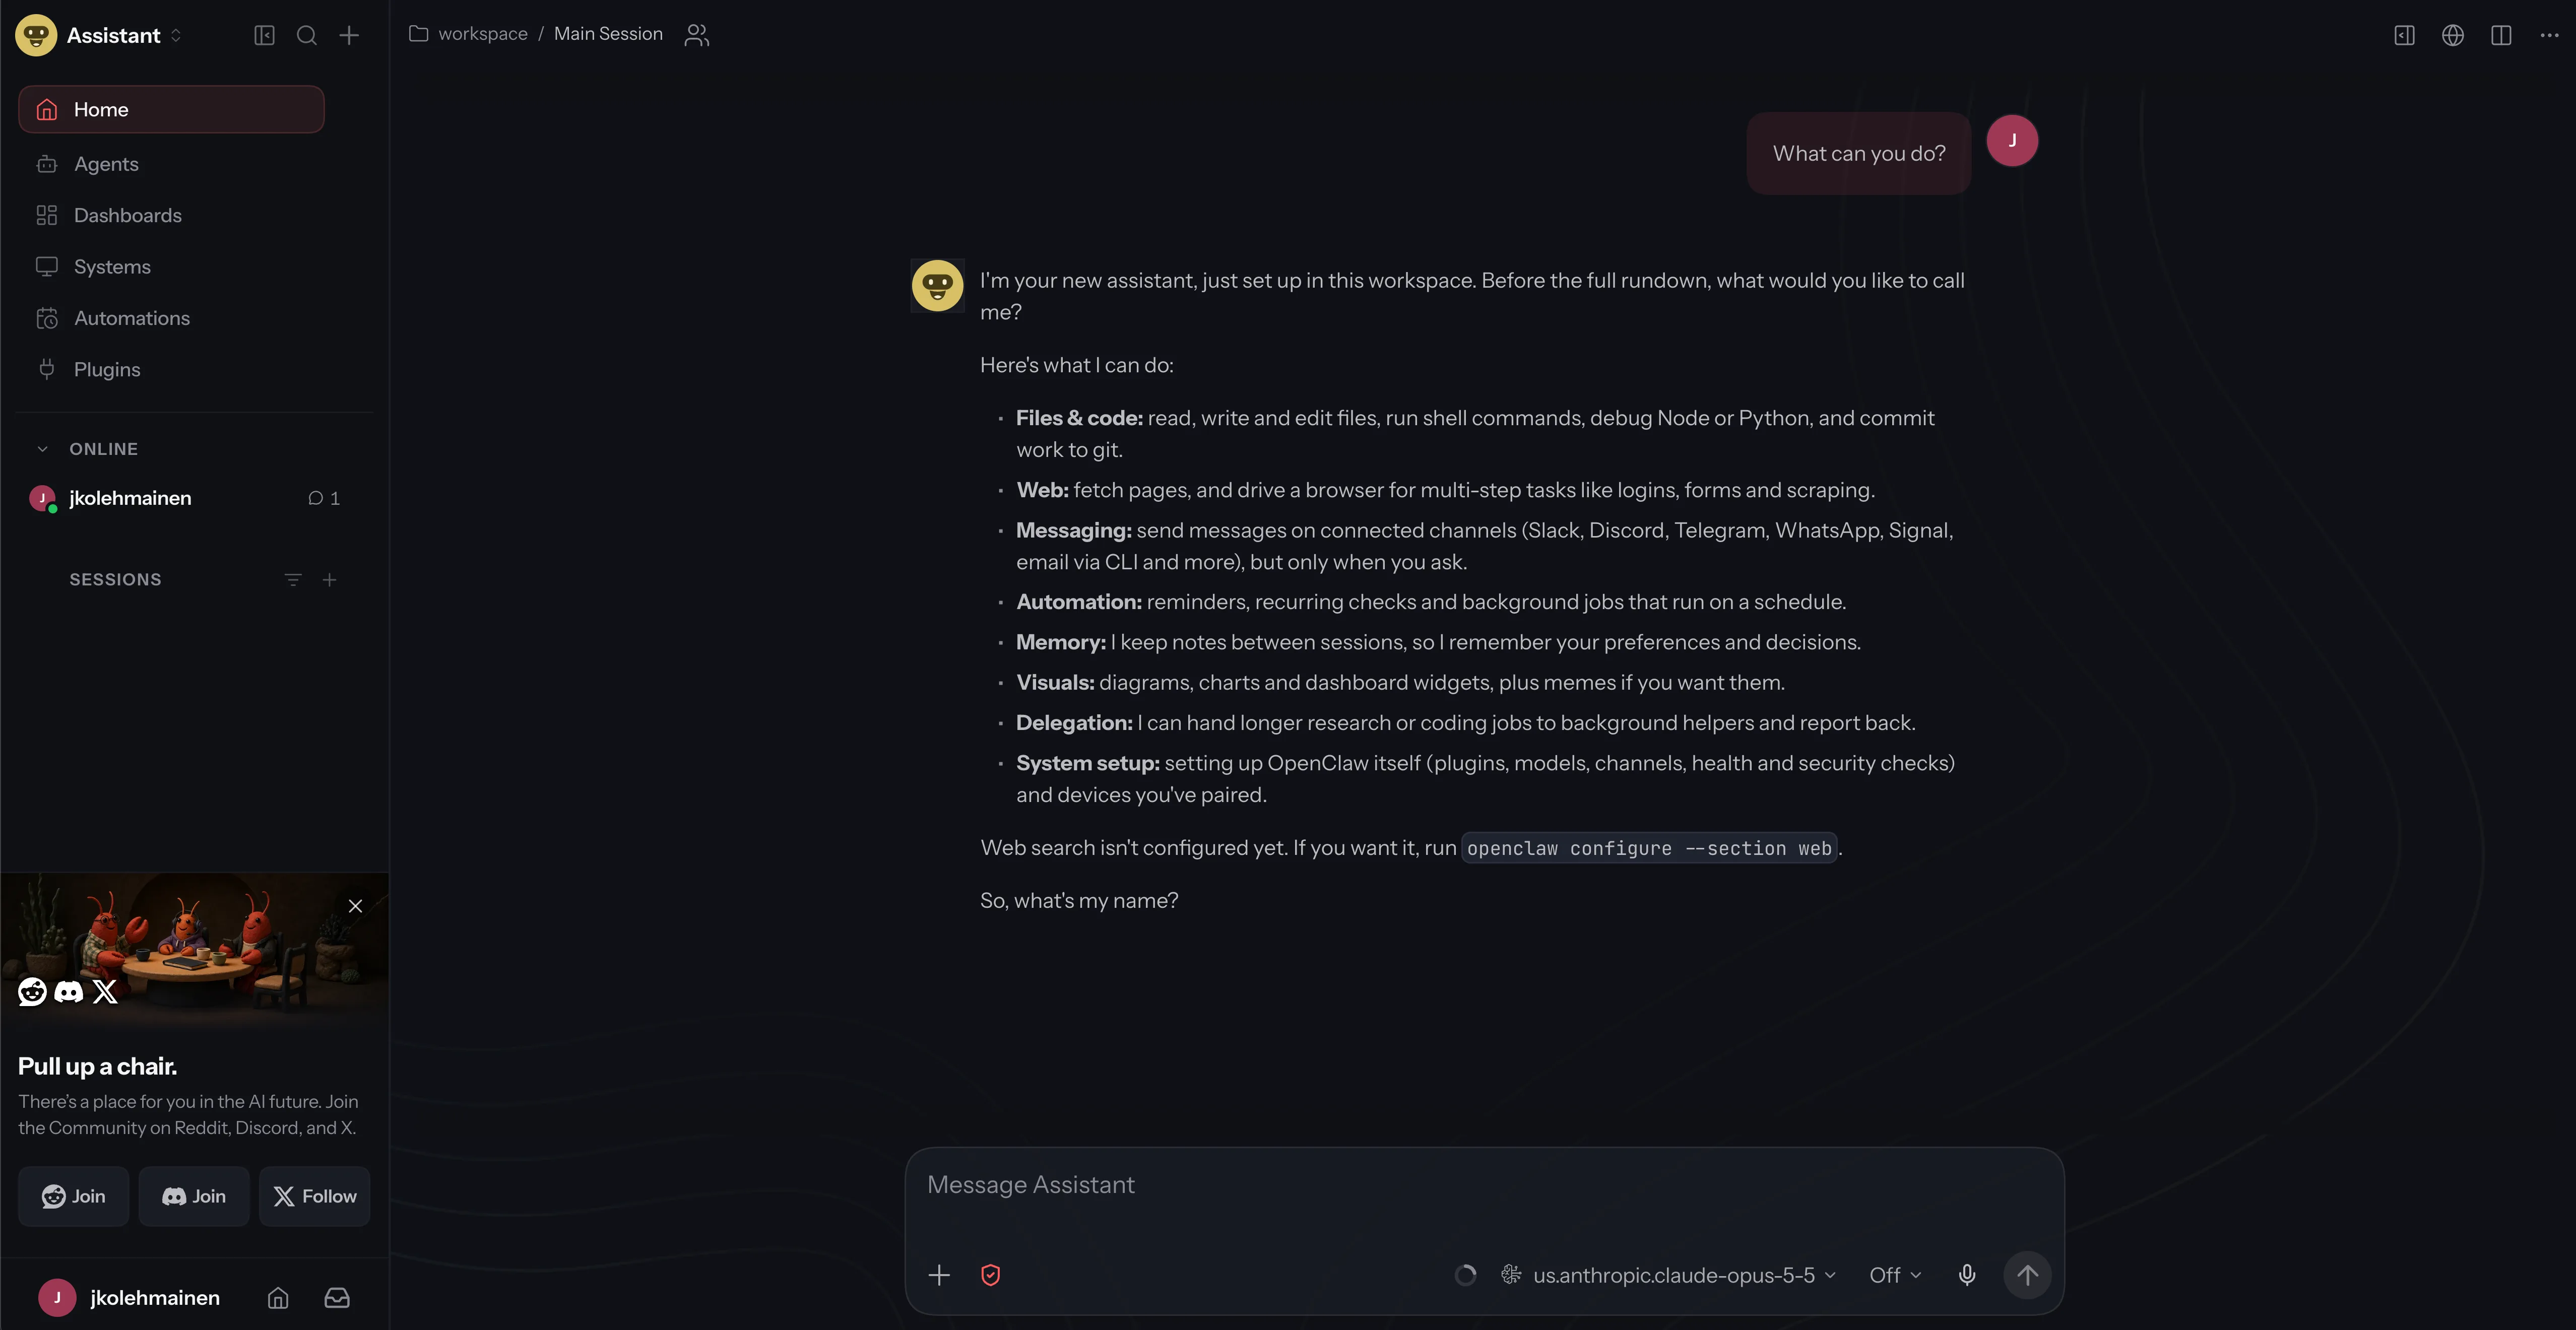
The Exposed Ports section of the output shows the URL of the web port. Open it and log in to the platform if asked. The Control UI opens as you, with admin rights.
Step 4: Give the assistant your tools#
The start script connects OpenClaw to the platform's MCP gateway. Through it, the assistant can use any MCP server that you add to your project, such as your issue tracker or your docs:
- Add the MCP server to your project as a connector, and connect your account to it there. See MCP connectors.
- Grant the connector in the sandbox policy, and choose which of its tools the assistant can use.
In sandbox.yaml, the grant goes under policy:
policy:
  # ... as in Step 1
  connectors:
    - connectorId: <connector-id>
      credentialId: <credential-id>   # only if the connector needs a login
      allowedTools: [search_issues, get_issue]
nexusctl connector describe <connector> --project <org>/<project> shows the connector's ID, its credentials, and its tools. Only the tools in allowedTools reach the assistant. Apply the change with nexusctl sandbox update <sandbox> --project <org>/<project> -f sandbox.yaml, with OPENCLAW_ADMIN set as in Step 2.
Your login for the MCP server stays in the platform. The sandbox sees the tools, never the token, and every tool call is recorded.
What the sandbox adds#
OpenClaw gives you the assistant. The sandbox decides what it can reach:
- No open port. The Control UI is behind your platform login, and OpenClaw sees who is calling.
- No model key in the sandbox. The OpenRouter key stays with the platform. Spending limits apply to it, and the spend is attributed to the sandbox. See Spending limits.
- Default-deny egress, with rules for each domain and each HTTP method. You choose what the assistant can reach beyond the model.
- Audit. Every request that the sandbox proxy handles is recorded with its policy decision. See Audit trail.
The platform also has a built-in OpenClaw sandbox template in the admin UI, with Slack as a channel. The spec in this tutorial is the same setup as a file, for one person, that you can keep in Git.
FAQ#
Can someone reach the Control UI without logging in?
No. The port is private, so every request goes through the platform login and a project access check before it reaches the sandbox.
Can I use another inference backend instead of OpenRouter?
Yes, if your organization has it. For most backends, change two things: provider in the policy, and the model in OPENCLAW_MODEL. OpenAI and Bedrock also need changes in the start script. The built-in OpenClaw template supports every backend, so use it as the reference.
How do I give the assistant a new tool or website?
The read-only rule already lets it read any website. To let it write to one, for example to POST to an API, add that domain to allowedDomains with the methods it needs. For MCP tools, see Step 4.
What happens to the assistant when the sandbox restarts?
The /data volume stays, so memory, workspace, and settings stay too. The script writes its own settings again, and the gateway starts.